Cybersecurity

Chainguard Survey: 77% of Security Chiefs Expect Exploit in 2026

Image
Chainguard Survey: 77% of Security Chiefs Expect Exploit in 2026

Kirkland, Wash. – October 14, 2026 -- Seventy-seven percent of security leaders expect an attacker to exploit a software vulnerability at their organization within 12 months, while 54% admit their companies knowingly leave high or critical vulnerabilities unpatched at least sometimes, according to a Chainguard report surveying 1,300 security leaders.

The report, titled The AI Exploit Gap, measures the distance between how fast AI-powered tools can find and chain vulnerabilities and how fast human teams can fix them. Ninety-one percent of respondents say AI-accelerated attacks have changed their job more than anything else in the past decade. Ninety-three percent worry their companies cannot remediate AI-driven exploits quickly enough.
Chainguard Launches Workspaces Beta to Isolate Coding Agents in microVMs

Image
Chainguard Launches Workspaces Beta to Isolate Coding Agents in microVMs

Seattle – October 14, 2026 -- Chainguard has launched Chainguard Workspaces in Beta, giving every developer and coding agent its own hardened microVM with no access to sensitive credentials and optional egress policies that block any connection a team has not approved.

Chainguard moves agent protection from the agent to its environment

The company argues that most coding agents today hold the same access as the developer who launched them, sitting next to credentials, cloud keys and production systems. Controls such as permission prompts and allowlists depend on the agent following the rules. Many developers now run a dozen agents or more at once, forcing teams to choose between granting broad access and approving prompts all day.

Chainguard CEO and Co-founder Dan Lorenc said teams are choosing between letting agents run next to production keys and babysitting them, and that "neither one scales."

Chainguard Adds Go, .NET Coverage and Zero-Day Patching to Libraries

Image
Chainguard Adds Go, .NET Coverage and Zero-Day Patching to Libraries

Seattle – October 14, 2026 -- Chainguard has extended its Libraries product to Go and .NET, added CVE remediation for JavaScript and Go, and begun delivering fixes for zero-day vulnerabilities on the day they are made public.

Chainguard Libraries for Go and .NET are available in Early Access. They give engineering teams and AI agents a managed endpoint for pulling dependencies without exposure to malicious packages.

Chainguard cites 76% AI-attack exposure among security leaders

Chainguard's AI Exploit Gap report found that 76% of cybersecurity leaders say their organization has experienced, or suspects it has experienced, an AI-driven attack in the last 12 months. Attackers publish malicious packages, hijack trusted ones, and register names of packages that do not yet exist, counting on developers and AI agents to install them unchecked. AI also lets anyone build and publish malicious packages or exploit CVEs and fresh zero-days.

Semperis: AI Used in 87% of Ransomware Attacks, Staff Threats Rise

Image
Semperis: AI Used in 87% of Ransomware Attacks, Staff Threats Rise

Hoboken – October 14, 2026 -- Threat actors weaponized artificial intelligence in 87% of ransomware attacks, and 40% of attacks involved psychological or physical threats against staff, according to the 2026 Ransomware Risk Report published by identity-focused cyber resilience company Semperis. The study surveyed only organizations that were hit by ransomware gangs in the past 12 months.

Attackers followed through on 53% of threats against employees

Bad actors used psychological intimidation in nearly 25% of all attacks across the U.S., UK, France, Germany, Italy, Spain, Singapore, Canada and Australia. In 53% of cases, victims reported that the hackers carried out their threats.

The personal toll was measurable: 23% of victims or family members were swatted, 25% of victims sought psychological and medical treatment, and 24% of victims or families hired personal security.

Armor CEO Tells GovWare CISOs: Govern AI, Don't Ban It

Image
Armor CEO Tells GovWare CISOs: Govern AI, Don't Ban It

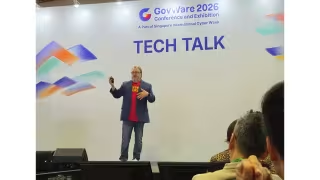
Singapore – October 14, 2026 -- Protiviti's February 2026 AI Pulse Survey found that 47% of large organizations have incomplete visibility into employees' use of AI tools, a gap Armor Founder and CEO Chris Drake cited at GovWare 2026 while arguing that CISOs should set conditions for AI adoption rather than ban it.

Drake said banning AI does not work and that ignoring it "is how the breach report gets written." In his Tech Talk Spotlights session, he said AI is already arriving through employees' browsers, productivity tools and machines, often without a separate security decision.

WEMIX Relaunches CertiK Bug Bounty With Payouts Up to $10,000

Image
WEMIX Relaunches CertiK Bug Bounty With Payouts Up to $10,000

Singapore – October 14, 2026 -- WEMIX has relaunched its joint bug bounty program with blockchain security firm CertiK, offering payouts of up to $10,000 per finding for vulnerabilities in its WEMIX3.0 Layer-1 blockchain. The program runs on CertiK's CertiK Hunt platform, and rewards scale with the severity of each finding.

Program targets WEMIX3.0 blockchain and governance smart contracts

Reports will focus on core ecosystem components: the WEMIX3.0 blockchain (DLT) and its Governance Smart Contracts. Rewards are denominated in USD and paid in Tether (USDT) on the Ethereum network.

Findings classed as "Critical" cover major risks such as total network outages or direct financial loss.

CrowdStrike, FBI Disrupt North Korea-Linked Laptop Farms Across U.S.

Image
CrowdStrike, FBI Disrupt North Korea-Linked Laptop Farms Across U.S.

United States – October 13, 2026 -- CrowdStrike's Counter Adversary Operations team and the FBI disrupted several U.S.-based laptop farms run by the DPRK-nexus adversary FAMOUS CHOLLIMA in late September 2026. The farms let North Korean operatives pose as remote workers at American companies while hiding their location and identity.

CrowdStrike says dozens of victim organizations were identified across the disrupted clusters. They span aerospace, energy, financial services, healthcare, cybersecurity, defense engineering, government technology and consumer technology. The company describes the targeting as sector-agnostic: any employer offering remote work is a revenue opportunity.

Tenable Nessus Adds Plugins to Clear False Positives on RLC Pro

Image
Tenable Nessus Adds Plugins to Clear False Positives on RLC Pro

Global – October 13, 2026 -- Tenable has released Nessus detection plugins built from CIQ's security advisories, so CVEs that CIQ has already fixed on Rocky Linux from CIQ Pro (RLC Pro) hosts now resolve in scan results instead of showing as unpatched.

Community advisories left CIQ fixes uncounted on pinned LTS hosts

RLC Pro LTS lets customers pin a host to a minor release and keep receiving security fixes on it. Even-numbered minor releases receive four years of security patching, and CIQ documents those fixes in its own advisories.

Tenable's existing Rocky Linux plugins draw on community Rocky Linux advisories, which do not include CIQ's. Nessus therefore compared a pinned host against the latest release, and a CVE that CIQ had already fixed on that release could still appear as unpatched. The same gap applied to packages CIQ adds beyond community Rocky Linux.

Coalfire Opens Buenos Aires Hub to Expand Global Delivery

Image
Coalfire Opens Buenos Aires Hub to Expand Global Delivery

Buenos Aires – October 13, 2026 -- Coalfire, a cybersecurity and compliance services provider, has opened Argentina Integrated Solutions (AIS) in Buenos Aires, adding delivery capacity to its global operating model.

AIS links Argentina-based staff to Coalfire teams and clients worldwide

The new location builds on Coalfire's existing international presence. AIS will connect Argentina-based professionals with Coalfire teams, clients and delivery capabilities around the world. Coalfire says this adds capacity for growth and strengthens local collaboration and continuity of service.

The company did not disclose headcount, investment size or a hiring timeline for the Buenos Aires site.

Rockwell Launches CompactLogix 5390 With 43% Smaller Footprint

Image
Rockwell Launches CompactLogix 5390 With 43% Smaller Footprint

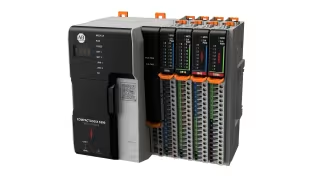
Milwaukee – October 13, 2026 -- Rockwell Automation (NYSE: ROK) has launched the CompactLogix 5390 controller, a unit with a footprint 43% smaller than the CompactLogix 5380 and security capabilities aligned to IEC 62443-4-2. The controller is the newest addition to the company's Integrated Architecture family and targets machine builders and OEMs.

CompactLogix 5390 builds in cybersecurity aligned to IEC 62443-4-2 and the EU Cyber Resilience Act

The controller combines built-in cybersecurity, integrated safety and higher performance on one control platform. Rockwell says its security capabilities are aligned to IEC 62443-4-2 and that the unit is ready for the EU Cyber Resilience Act. The aim is to let machine builders address evolving global requirements without adding complexity to machine architecture.