Cybersecurity

Advantech, DEKRA Sign MOU as EU CRA Compliance Pressure Builds

Image
Advantech, DEKRA Sign MOU as EU CRA Compliance Pressure Builds

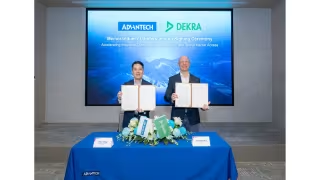
Taipei – October 16, 2026 -- Advantech's AFE-E630 industrial edge system has received an Attestation of Conformity from DEKRA for IEC 62443-4-2 SL2 requirements, the first result of a new memorandum of understanding (MOU) between the two companies on industrial cybersecurity compliance.

The MOU, announced as the EU Cyber Resilience Act (CRA) enters its implementation phase, targets industrial equipment and Edge AI products bound for global markets. The partners aim to help system integrators and end customers meet CRA requirements and international standards such as IEC 62443, cut compliance risk and shorten time to market.
Cyfendo Targets SMB Code Security as FBI Tallies $20.9B Losses

Image
Cyfendo Targets SMB Code Security as FBI Tallies $20.9B Losses

Mountain View – October 15, 2026 -- Cyfendo, a Silicon Valley application-security startup, has launched an AI platform that investigates software vulnerabilities and prepares tested patches for small businesses, as the FBI's 2025 Internet Crime Report recorded about $20.88 billion in reported losses across 1,008,597 complaints.

Cyfendo reports four critical issues per scanned codebase

According to Cyfendo's own scan data, the company finds an average of four critical-severity issues per codebase, and roughly seven in ten findings are rated high or critical. The company states these results come from projects it scanned, not a representative survey of business applications.

CGI: Frontier AI Shifts Cyber Bottleneck to Executive Decision Speed

Image
CGI: Frontier AI Shifts Cyber Bottleneck to Executive Decision Speed

Global – October 15, 2026 -- The main constraint on cyber defense is moving from vulnerability discovery to organizational decision speed, according to CGI's Pierre Le Calvez, as frontier models such as Anthropic's Claude Mythos and OpenAI's GPT-5.6 Sol advance.

Approval delays outpace detection in security operations

In a blog titled "Defending at the speed of frontier AI: Lessons from the Fable shutdown and what to do in the next 60 days," Le Calvez argues that AI-assisted tools now surface vulnerabilities within minutes and clarify their impact within hours. The delays now sit in approval processes, competing business priorities, resource constraints and fragmented ownership rather than inside the security operations center.

Resilient organizations share five operating traits

The blog lists the characteristics of resilient organizations:

CompTIA: 98% of Firms Rank AI Risk Management Essential

Image
CompTIA: 98% of Firms Rank AI Risk Management Essential

Downers Grove, Ill. – October 15, 2026 -- Some 98% of companies surveyed by CompTIA say risk management is important within organizational AI policies, as the focus of enterprise AI shifts from adoption to execution risk, according to the trade group's new research brief "Practical Implications of AI Safety."

About six in 10 organizations move toward enterprise-wide AI implementation

CompTIA's "Corporate AI Adoption" report found that roughly 60% of organizations are moving from experimentation and individual productivity use cases toward enterprise-wide deployment. Cybersecurity concerns rank as the second-largest challenge to AI adoption. Only finding the right balance between human employees and AI-powered tools and agents ranks higher.

Security-related policy elements draw near-universal support

Among surveyed companies, 96% cited data protection and privacy as important, and 95% cited governance. Risk management led at 98%.

Biomemory Opens Early Access to DNA Shield Data Protection

Image
Biomemory Opens Early Access to DNA Shield Data Protection

Paris – October 15, 2026 -- Biomemory has launched DNA Shield, a managed service that stores encrypted customer data as synthetic DNA in offline custody, and opened its Early Access Program to organizations that need an independent layer for critical digital assets. It is the company's first commercial product.

The service is built as a separate layer held at rest, apart from the active control plane and outside the network-reachable attack surface. Biomemory pitches it at information that must stay trustworthy for years or decades, including against risks from advances in artificial intelligence and quantum computing.

Threat Intelligence Market to Hit $24.1B by 2032 at 19.52% CAGR

Image
Threat Intelligence Market to Hit $24.1B by 2032 at 19.52% CAGR

Noida – October 14, 2026 -- The global threat intelligence market is projected to grow from USD 5,789.50 million in 2024 to USD 24,108.25 million by 2032, a CAGR of 19.52%, according to a Credence Research Inc. report.

Rising attacker sophistication, expanding cloud and identity attack surfaces and growing automation in security operations are driving demand. Enterprises want intelligence feeds, investigation platforms and managed expertise that help analysts prioritize material threats rather than add to alert volume.

North America holds 42% of demand, Asia Pacific about 25%

The report estimates North America at roughly 42% of global demand, supported by large enterprises, federal and regulated buyers and a dense cybersecurity vendor base. Procurement there increasingly emphasizes measurable detection improvement and integration with existing controls.

Censys: Exposed AI Infrastructure Jumps 63% in Nine Months

Image
Censys: Exposed AI Infrastructure Jumps 63% in Nine Months

Ann Arbor – October 14, 2026 -- Internet-facing AI infrastructure grew 63% in nine months to nearly 268,000 systems, according to the fifth annual State of the Internet Report from Censys. The report also counts roughly 134,000 Internet-exposed hosts running industrial control systems (ICS). About 70% of those sit on consumer and mobile networks, which complicates efforts to identify their owners and close the exposure.

n8n and OpenClaw dominate exposed AI tooling

The Censys Advanced Research Collective (ARC) drew on historical and real-time data from the Censys Internet Map. The exposed AI category covers chatbots as well as the tools that connect AI to data, applications and user accounts.

Aura Business Taps Climb to Sell BYOD Security to MSPs

Image
Aura Business Taps Climb to Sell BYOD Security to MSPs

Boston – October 14, 2026 -- Aura Business, the business division of Aura (ASX: AXQ), has signed a distribution partnership with Climb that gives Climb's network of resellers and managed service providers (MSPs) access to Aura Business's new identity-centric BYOD security solution.

Climb is a global specialty technology distributor focused on security, data management, connectivity, cloud and software. Its customers can access Aura Business immediately through the Climb marketplace.

Omdia data shows 55% of MSPs have had a BYOD-related security incident in 24 months

Aura cited Omdia research to frame the opportunity. According to the figures, 65% of MSPs are seeing demand for BYOD management, yet only 24% monitor employee-owned devices. Some 55% have experienced a BYOD-related security incident in the past 24 months.

Blackbird.AI Launches RAV3N Radar to Push Narrative Alerts to Slack

Image
Blackbird.AI Launches RAV3N Radar to Push Narrative Alerts to Slack

New York – October 14, 2026 -- Blackbird.AI has launched RAV3N Radar, an agent-driven service that delivers continuous narrative-threat alerts directly into Slack, as Gartner forecasts that enterprise spending on fighting misinformation and disinformation will surpass $30 billion by 2028.

RAV3N Radar provides 24/7 monitoring of the digital landscape. It covers landscape insights, threat actors, velocity signals, topics and escalation detection. The service runs on RAV3N Agent, Blackbird.AI's context-aware narrative intelligence agent, and delivers briefs to Slack or email.

Each alert documents six data points on a narrative

Every brief or real-time alert records:

Chainguard Launches Harness AI Bug Hunter on Claude Marketplace

Image
Chainguard Launches Harness AI Bug Hunter on Claude Marketplace

Seattle – October 14, 2026 -- Chainguard has launched Chainguard Harness, a cyber harness that runs frontier AI models such as Anthropic's Claude Mythos 5.1 against a live build of a customer's application and delivers only reproduced vulnerabilities, each paired with an engineer-reviewed fix. The product is available through the Claude Marketplace by Anthropic, so enterprises can buy it with their existing Anthropic commitment.

Harness tests running applications in isolated microVMs instead of scanning static code

Harness connects to a team's repository through the Guardener GitHub app, builds the application as it ships, and boots it in an isolated microVM. A frontier model then probes the running instance the way an attacker would. Chainguard says this approach surfaces logic flaws, injection paths and resource exhaustion bugs that appear only at runtime and that traditional static scanners miss.