Ransomware Shifts to Directory Destruction, Bypassing 47.8% of Scans
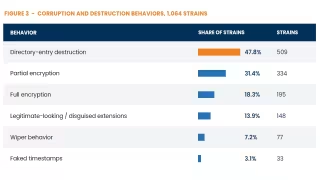
Holmdel, N.J. – September 30, 2026 -- Index Engines' CyberSense Research Lab found that 47.8% of 1,064 ransomware strains detonated in the first half of 2026 relied on directory-entry destruction, more than double the 18.3% that used full encryption, marking a shift away from techniques that trigger standard security scans.
Attackers now suppress the telltale signs security tools rely on
The lab documented new ransomware built to preserve file extensions and timestamps, maintain low entropy, and encrypt only selected sections of files slowly enough to avoid detection thresholds. One variant, Encoder, destroyed file content while leaving names, sizes, timestamps, and entropy readings unchanged, according to Jim McGann, CMO of Index Engines. A surface scan would report that data as clean, McGann said, while CyberSense identified the corruption by analyzing file content and structure directly.