Cybersecurity

ScamAdviser's Watchmen Wins Scam Fighter Award at GASA Summit
Image
ScamAdviser's Watchmen Wins Scam Fighter Award at GASA Summit

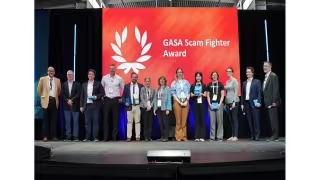
San Francisco – September 22, 2026 -- ScamAdviser's Watchmen platform won the Scam Fighter Award at the Global Anti-Scam Summit (GASS) America 2026, organized by the Global Anti-Scam Alliance (GASA) in San Francisco, for its role in cutting fraud detection-to-takedown times from weeks to under 8 hours.

Watchmen deployments contributed to a 38% drop in investment scam financial losses

In deployments with financial regulators, law enforcement agencies, and municipal governments, Watchmen demonstrated national-level impact, including a 38% reduction in the share of investment scam financial losses. The system uses multi-layered filtering, expert rule engines, and Large Language Model (LLM) semantic analysis to monitor corporate communication channels and social media platforms for brand impersonation, triggering automated takedown mechanisms once threats are confirmed.
Siemba Launches MCP Server to Run Pentests via AI Chat

Image
Siemba Launches MCP Server to Run Pentests via AI Chat

Atlanta – September 22, 2026 -- Siemba has launched general availability of Siemba MCP, a Model Context Protocol server that lets security and engineering teams run penetration tests and generate finished security analysis by chatting directly with AI assistants, eliminating the need for a separate dashboard login.

Six packaged skills replace manual dashboard analysis

Siemba MCP ships as a single plugin containing a connector and six named skills: Test Analysis, Kill Chain, Critical Briefing, Remediation Plan, Attack Surface, and CISO Report. Test Analysis reads login screenshots to diagnose failed authenticated test runs caused by bad credentials or unexpected multi-factor prompts. Kill Chain maps individual findings into full attack paths, rating each chain by its weakest link rather than raw severity and naming the single fix that breaks the most chains at once.

Palo Alto Networks Launches Continuous AI Defense with Anthropic, OpenAI

Image
Palo Alto Networks Launches Continuous AI Defense with Anthropic, OpenAI

Santa Clara, Calif. – September 22, 2026 -- Palo Alto Networks has launched Unit 42 Continuous Frontier AI Defense, a new agentic offensive security service built on Anthropic's Claude Mythos 5 and OpenAI's GPT-5.6-Cyber models, aimed at helping enterprises find and fix exposures before attackers exploit them at machine speed.

The service responds to a shift in attacker capability: threat actors using AI have compressed breach cycles by nearly 97% in some cases, cutting the time from vulnerability discovery to exploitation from weeks to hours, according to Palo Alto Networks.

Ridgeway Pharmacy Discloses Third-Party Website Breach Exposing Patient Data

Victor, Montana – – September 21, 2026 -- Ridgeway Pharmacy, Ltd. has confirmed that a vulnerability in its vendor-supported website allowed an unauthorized third party to gain elevated access, potentially exposing patient names, dates of birth, addresses, prescription and health information, insurance details, and, for some individuals, payment card data.

Ridgeway confirms breach originated in vendor-managed site, not internal systems

The pharmacy said the compromise was limited to its externally developed website and did not touch Ridgeway's own internal infrastructure. External cybersecurity and forensic specialists were brought in after operational irregularities were first detected on the site.

Siemba Automates IDOR Testing Across Full API Collections

Image
Siemba Automates IDOR Testing Across Full API Collections

Atlanta – September 20, 2026 -- Siemba has launched automated testing for insecure direct object reference (IDOR) flaws, cutting the time to scan a 200-endpoint API collection to under an hour, a task the company says has typically taken human testers days or weeks.

IDOR ranks first among OWASP's API Security Top 10 risks

IDOR, classified by OWASP as broken object level authorization, occurs when an endpoint fails to verify that a caller-supplied identifier belongs to them, allowing a single changed number in a request to expose another user's data. Siemba's Chief Security Officer Sandhya Prashanth said the flaw "drives a huge share of real-world breaches" and requires little more than systematic testing across every endpoint to detect.

Siemba Named in Three Gartner Hype Cycle Reports for Third Straight Year

Image
Siemba Named in Three Gartner Hype Cycle Reports for Third Straight Year

Atlanta – September 20, 2026 -- Siemba, an offensive security provider, has been named a Sample Vendor for Penetration Testing as a Service (PTaaS) in three separate 2026 Gartner Hype Cycle reports, marking the third consecutive year the company has secured this recognition across all three publications.

Siemba earns placement across security operations, application security and XaaS research

The company was cited in the 2026 Hype Cycle for Security Operations, the Hype Cycle for Application Security, and the Hype Cycle for XaaS. The Security Operations report examines the growth of Continuous Threat Exposure Management (CTEM) as a priority for enterprise security teams, while the Application Security report covers how AI transformation and agentic applications are reshaping enterprise risk. The XaaS report addresses the shift toward platform-driven, everything-as-a-service consumption models in IT.

Arcjet Launches Runtime Security Product for Production AI Agents

San Francisco – – September 19, 2026 -- Arcjet has launched agent runtime security, a new product designed to give engineering and security teams visibility and control over AI agents operating inside production systems. The platform targets agents that read and write to databases, process refunds, call APIs, and take autonomous actions across multiple systems on behalf of users.

Arcjet builds its product around three functions: observe, enforce, and audit

The observe layer lets teams ingest agent activity without changing application code, using existing OpenTelemetry tooling or, for Claude users, the Claude Compliance API. Arcjet connects actions across sessions into a single workflow view, capturing prompts, tool call parameters, session metadata, identity, and security decisions, and maintains an inventory of agents and applications running in a given environment.

Qtonic Quantum Launches QShield After 4,107-Check Endurance Test

Image
Qtonic Quantum Launches QShield After 4,107-Check Endurance Test

Miami – – September 19, 2026 -- Qtonic Quantum Corp launched QShield, a software-only post-quantum packet runtime for Linux hosts, and opened paid, operator-led engagements to enterprise and government buyers following a completed 72-hour endurance run that logged 4,107 successful periodic checks and zero failures.

QShield Launches With a Published, Verifiable Test Record

The September 13-16 endurance run connected two Linux hosts across separate AWS availability zones in Oregon, checking connectivity, service status and a 64 KiB transfer roughly every 63 seconds. All 4,107 checks reported success, zero ping loss was recorded, and both daemon paths hashed to the identified build at harvest with zero restarts. The 72-hour gate closed at 04:29 UTC on September 16, and the operator left the overlay running. Qtonic published the run log, build hash, checksums and a verifier that passes 11 of 11 checks so buyers can inspect the result independently.

Leidos Wins Corrected $926M Navy Network Contract Option Year

Image
Leidos Wins Corrected $926M Navy Network Contract Option Year

Reston, Va. – September 19, 2026 -- The U.S. Department of the Navy has awarded Leidos $926 million for the second option year of its Next Generation Enterprise Network Service Management, Integration and Transport contract, correcting an earlier figure of $875 million issued in a prior release.

Leidos secures $926 million to manage networks for 650,000 Navy and Marine Corps personnel

Under the award, Leidos will continue managing more than 425,000 devices across over 2,500 sites worldwide, supporting user access, IT operations and transformation activities on the Navy Marine Corps Intranet (NMCI), the Outside the Continental United States Navy Enterprise Network (ONE-Net) and the Marine Corps Enterprise Network (MCEN).

First Health Advisory Launches Resilience360 for Hospital Continuity

Image
First Health Advisory Launches Resilience360 for Hospital Continuity

Washington – September 18, 2026 -- First Health Advisory has launched Resilience360, a consulting program designed to validate whether hospitals and health systems can keep clinical operations running during cyberattacks, technology outages, third-party failures, and natural disasters.

Program targets the gap between disaster recovery plans and actual clinical continuity

Healthcare organizations have invested heavily in disaster recovery, incident response, and emergency preparedness, but many have not validated how clinical and operational workflows will continue functioning while systems are being restored, according to First Health Advisory. Resilience360 is built to close that gap by testing the people, processes, and workflows required to sustain patient care throughout a disruption, rather than adding another compliance framework.