MQTT Security Hinges on Broker Architecture, Not Encrypted Ports
Image
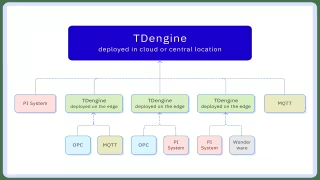
Global – October 29, 2026 -- Secure MQTT telemetry collection across IT/OT boundaries depends on the architecture around the broker, clients, identity and operations, not on choosing an encrypted port, according to TDengine guidance on industrial data ingestion.
Broker placement decides which systems need a route to OT
The broker can sit near sources, in an industrial DMZ or in another approved service zone, depending on the site's threat model, reliability needs and operating ownership. An IT subscriber should connect only to an approved broker endpoint, not to controllers or the wider OT network. The guidance cites NIST's Guide to Operational Technology Security, which requires OT designs to weigh performance, reliability and safety alongside cybersecurity risk.