Global – October 29, 2026 -- OX has launched Agent Activity in early access, giving security teams step-by-step runtime visibility into AI agent sessions across its OX.VibeSec and OX.Cloud platforms, with more than 100 built-in guardrail policies.
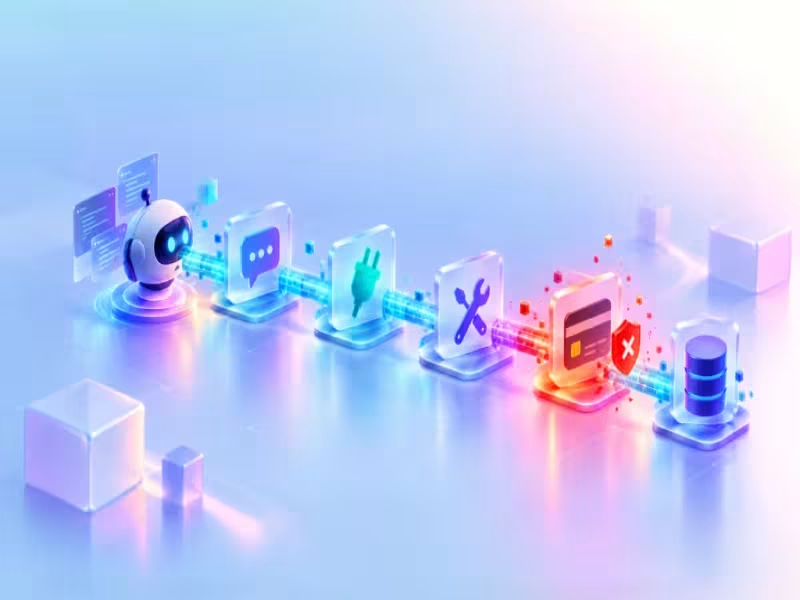
Agent Activity traces each session from prompt to data access
For every agent session, security teams can follow the full chain of actions from start to finish. The tool records prompts and responses, the MCP servers and tools the agent called and in what order, and whether the agent held read or write access. That distinction separates an agent that views a ticket from one that modifies it, or one that reads Slack from one that posts to it.
It also flags when an agent interacts with PII, secrets, tokens, or financial data, and when that data risks leaving where it belongs.
Custom guardrails let teams flag or block violations
Teams can build runtime policies around the AI models in use, the MCP servers agents can reach, and the skills they can combine. One example from OX: stopping a specific model from using a set of MCP servers alongside a skill that touches sensitive internal data.
Each team decides whether a violation is surfaced for review or stopped outright, and sets the severity to match its risk tolerance. The product ships with more than 100 out-of-the-box policies, with more planned.
OX adds a LiteLLM connector and spans endpoint to production
Agent Activity runs across both OX.VibeSec and OX.Cloud, giving teams a single view of agent behavior from developer endpoints through production workloads. A new LiteLLM connector brings LLM proxy traffic into the same view.
Agent Activity is available now in early access for OX customers, with the experience set to evolve ahead of general availability.